The Azure Security Engineer Roadmap (2027)
If your security roadmap still says AZ-500, it's pointing at an exam you can't book. Microsoft retired it on August 31, 2026. The certifications around it changed too, and so did the portal most security operations teams work in.
This roadmap covers what changed, which certification fits which job, and three lanes into Azure security. You pick a lane by the job you have today. Each lane comes with one proof project, the commands that define "done", and the hands-on labs to practise it.
Bookmark it. It's meant to be used as a checklist, not read once.
What Changed in 2026
| Change | What it means for you |
|---|---|
| AZ-500 retired on August 31, 2026 | You can't book it or renew it. If you already hold it, it stays valid until its expiry date, then shows as expired. |
| SC-500 replaced it | SC-500: Implementing End-to-End Security Controls for Cloud and AI Workloads earns the Cloud and AI Security Engineer Associate certification. It became available in July 2026. |
| SC-500 adds AI security | A whole section covers securing AI: Microsoft Purview DSPM for AI, Copilot Studio agents, Microsoft Entra Agent ID, Defender for AI services and guardrails in Microsoft Foundry. |
| SC-100 prerequisites changed | The Cybersecurity Architect Expert now needs one of SC-300, SC-200 or SC-500. |
| Sentinel moves to the Defender portal | After March 31, 2027, Microsoft Sentinel is no longer supported in the Azure portal and is available only in the Microsoft Defender portal. Learn it there from day one. |
Sources: Microsoft's retired exams list, the SC-500 study guide, the Cybersecurity Architect Expert page and the Sentinel retirement timeline.
Note: Security engineer is rarely your first cloud job. It's usually your second or third. The SC-500 study guide expects "practical experience in administration of Azure and hybrid environments", and interviewers will ask you to secure something you've already built. Every lane below assumes you can run the Azure basics, or that you're learning them alongside. If you're not there yet, start with How to Learn Azure in 2027.
The Certification Map
| Certification | Exam | Who it's for | Level |
|---|---|---|---|
| Security, Compliance, and Identity Fundamentals | SC-900 | Anyone new to Microsoft security. Optional. | Fundamentals |
| Identity and Access Administrator | SC-300 | Helpdesk, Microsoft 365 admins, sysadmins who know Active Directory | Associate |
| Security Operations Analyst | SC-200 | SOC analysts, incident responders | Associate |
| Cloud and AI Security Engineer | SC-500 | Azure admins, network engineers, engineers from AWS or Google Cloud | Associate |
| Information Security Administrator | SC-401 | People who protect data with Microsoft Purview | Associate |
| Cybersecurity Architect Expert | SC-100 | Engineers designing security across an organization. Needs SC-300, SC-200 or SC-500 first. | Expert |
You don't need all of them. You need one associate certification that matches your lane, plus a project that proves you can do the work.
Pick Your Lane
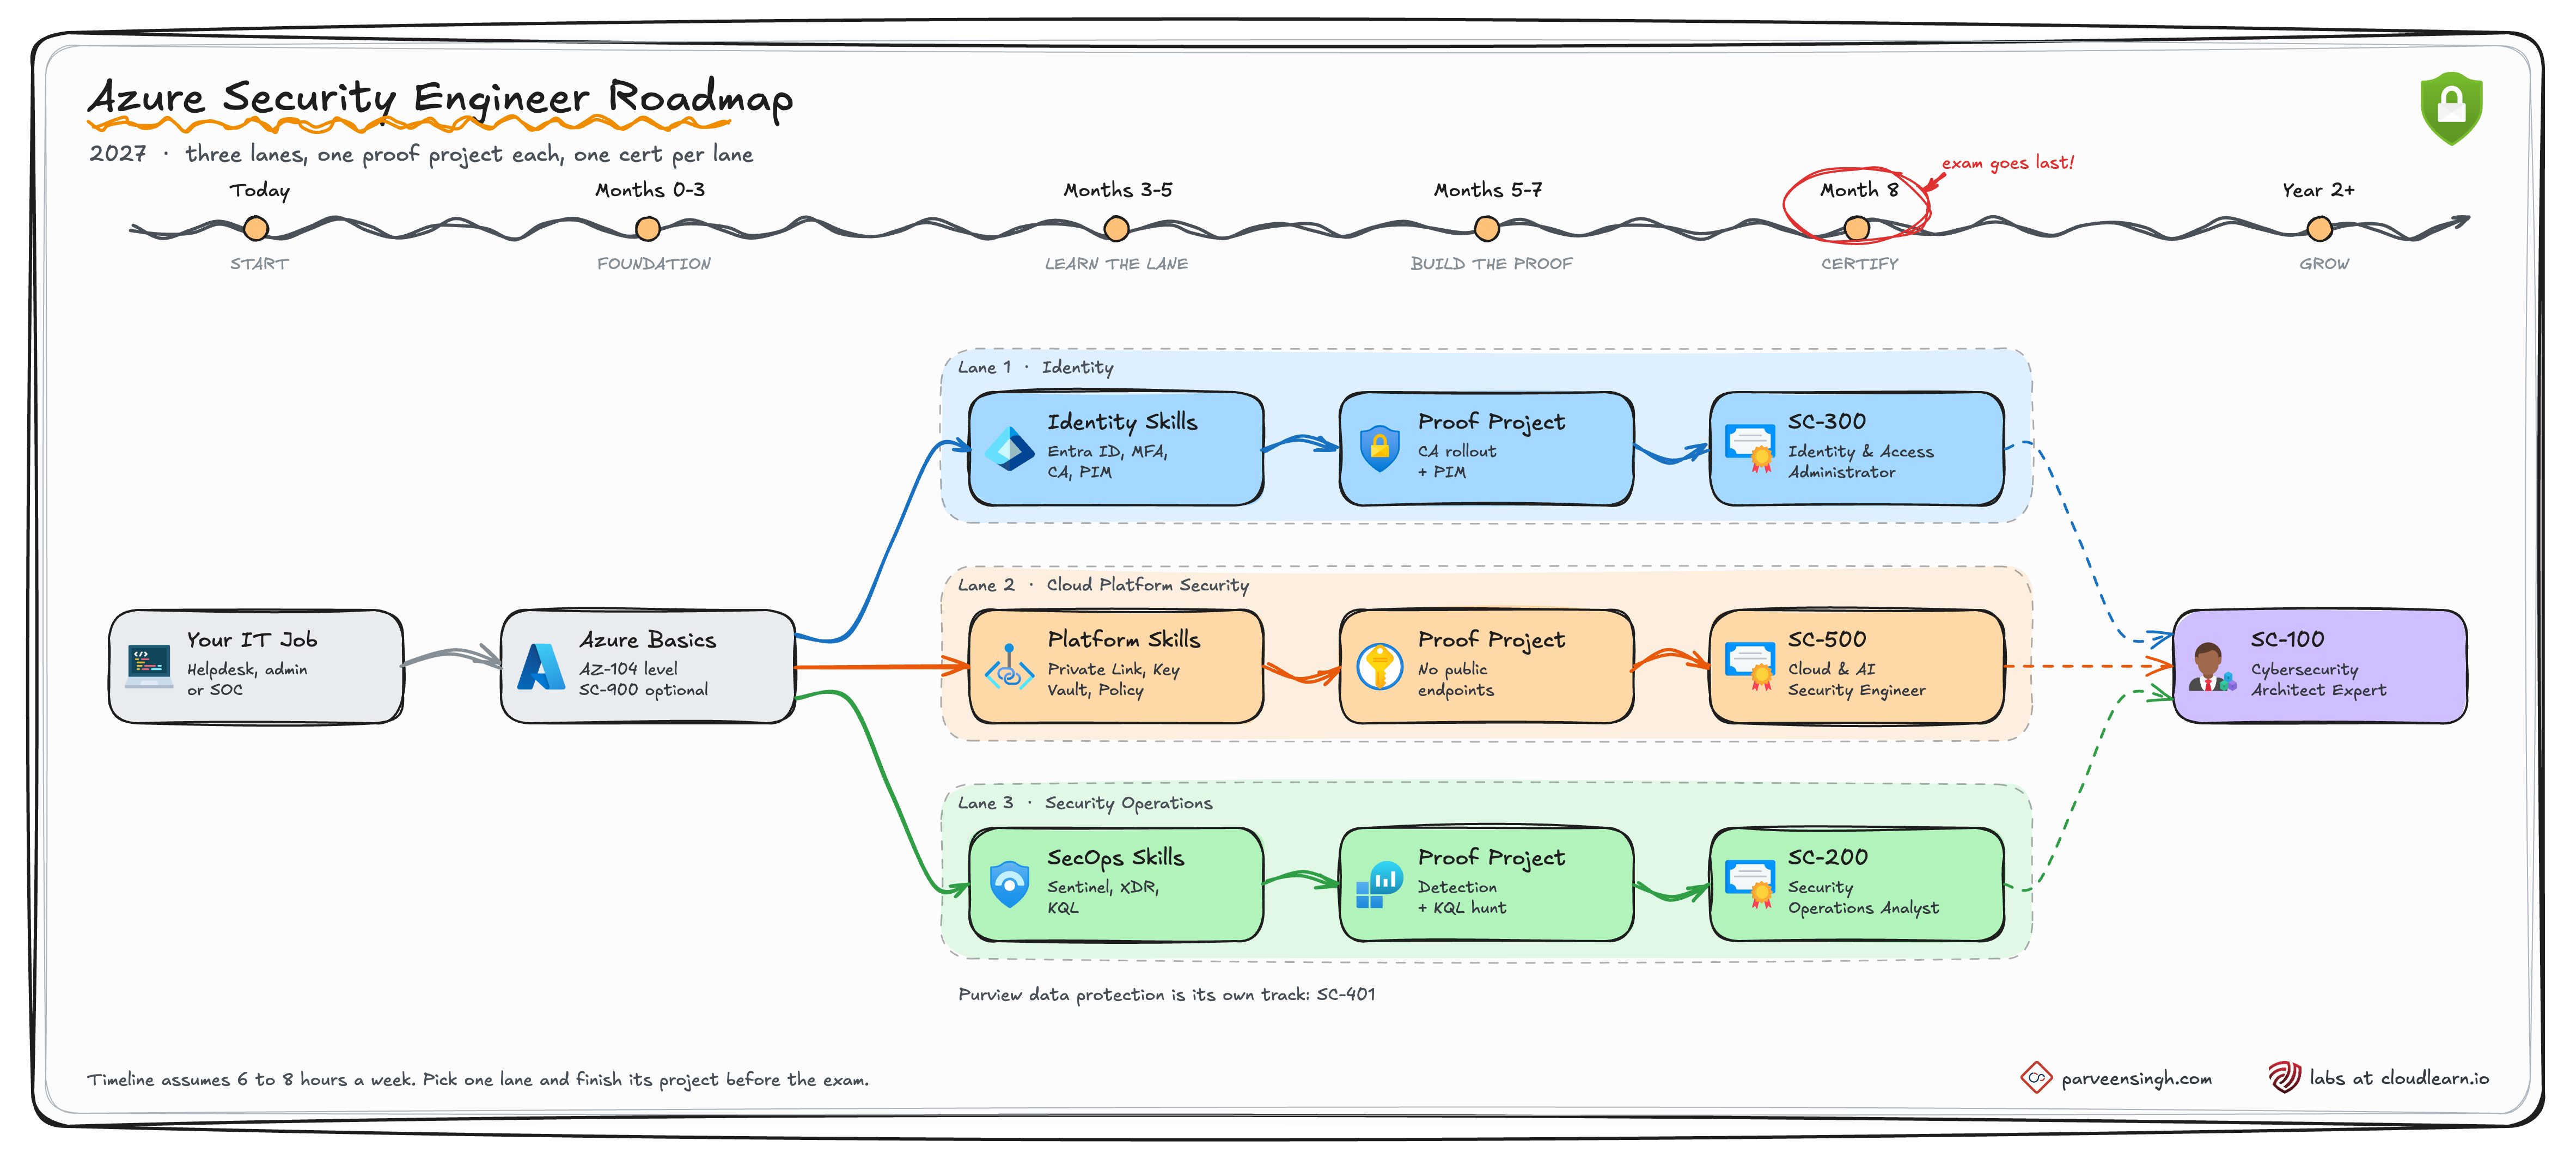
Click the roadmap to zoom in.
| Lane | Typical starting job | Associate cert | Daily work |
|---|---|---|---|
| 1. Identity | Helpdesk, Microsoft 365 admin, sysadmin with Active Directory | SC-300 | Entra ID, Conditional Access, MFA and passwordless, Privileged Identity Management (PIM), access reviews |
| 2. Cloud platform security | Azure admin, network engineer, engineer from AWS or Google Cloud | SC-500 | Network segmentation, private endpoints, Key Vault, Azure Policy, Defender for Cloud, securing AI workloads |
| 3. Security operations | SOC analyst moving from alert triage into engineering | SC-200 | Defender XDR, Sentinel, writing detections, hunting with KQL, incident response |
Find your row first. If two rows fit, pick the one closest to the work you already do every day. You can move lanes later. The skills overlap more than the certification names suggest.
The rest of this post follows the roadmap from left to right, one stage at a time. The timings assume 6 to 8 hours a week next to a full-time job. If you can give it more, every stage gets shorter, but the order stays the same.
Stage 0: Start (Today)
Before you study anything, be honest about where you're starting. Take ten minutes and answer these:
| Question | If the answer is no |
|---|---|
| Can you sign in to the Azure portal and find a resource group? | Start Stage 1 from the beginning |
| Can you explain the difference between a Microsoft Entra ID role and an Azure RBAC role? | Spend extra time on identity in Stage 1 |
| Have you created a virtual network and a VM with the Azure CLI? | Do the networking and compute labs in Stage 1 |
| Have you written a KQL query against real logs? | Add the KQL lab to Stage 1 |
| Does your current job touch identity, Azure infrastructure or security alerts? | Pick the lane closest to what you do now, not the one that sounds best |
If you can answer yes to all five, skim Stage 1 and go straight to your lane.
Stage 1: Foundation (Months 0 to 3)
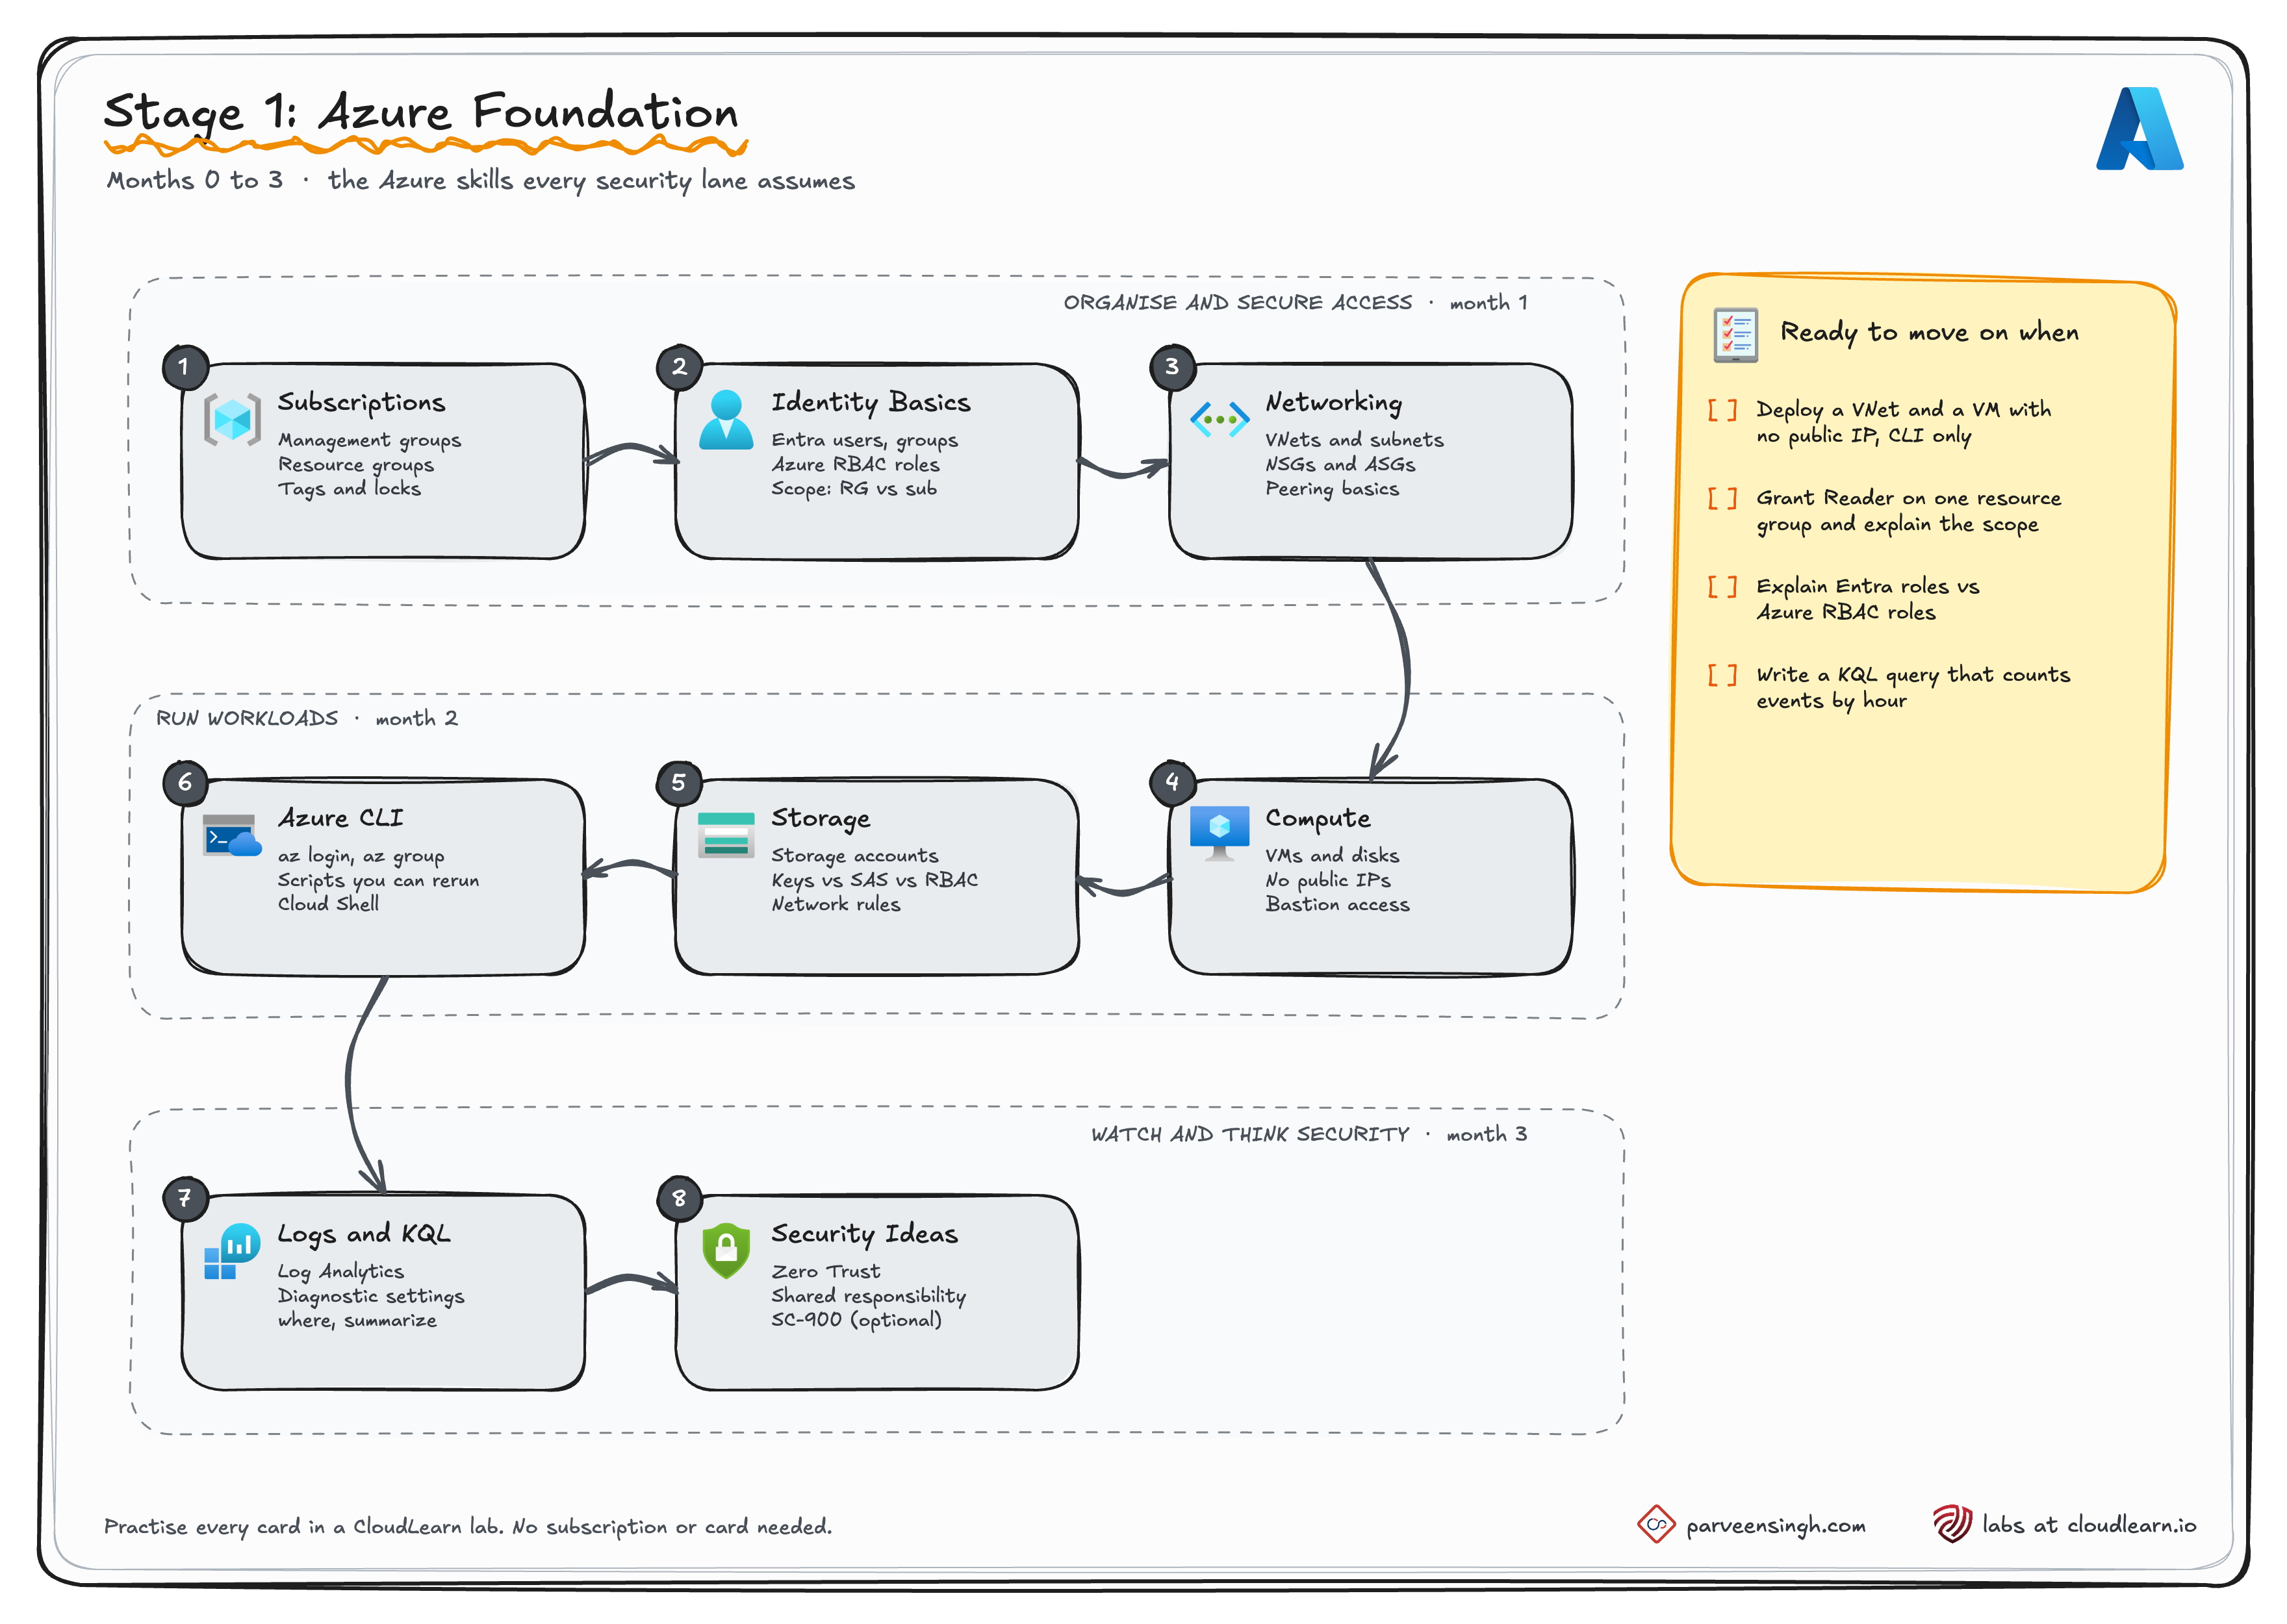
Every lane assumes you can run Azure. This is the stage most people skip, and it's the one interviewers find first. You don't need to pass AZ-104, but you need the skills it tests.
| Learn | Microsoft Learn | CloudLearn lab |
|---|---|---|
| Subscriptions, resource groups, tags and locks | AZ-104 prerequisites | Implementing Azure Resource Locks |
| Entra ID users, groups and Azure RBAC | Manage identities and governance · What is Azure RBAC? | Entra ID: Create Users, Groups and Assign Roles |
| Virtual networks, subnets and NSGs | Configure and manage virtual networks | Implement NSGs and ASGs |
| Virtual machines and secure access | Virtual networks overview | Creating Your First Virtual Machine (free) · Secure VM Access with Azure Bastion |
| Storage accounts | AZ-104 prerequisites | Getting Started with Azure Storage Account |
| The Azure CLI | Get started with the Azure CLI | Used in every lab above |
| Logs and KQL basics | Log Analytics overview | Introduction to KQL in Azure Log Analytics |
| Security concepts (optional) | SC-900: Security, compliance and identity concepts |
You're ready for Stage 2 when you can:
- Deploy a virtual network, a subnet and a VM with no public IP, using only the Azure CLI.
- Give a user Reader access to one resource group, and explain why you didn't use a subscription-level role.
- Explain the difference between a Microsoft Entra ID role and an Azure RBAC role in one sentence each.
- Write a KQL query that counts sign-ins or events by hour.
If you're new to the command line, Bash Scripting for Beginners covers enough to script the first point.
Stages 2 and 3, Lane 1: Identity
Learn the lane: months 3 to 5. Build the proof: months 5 to 7.
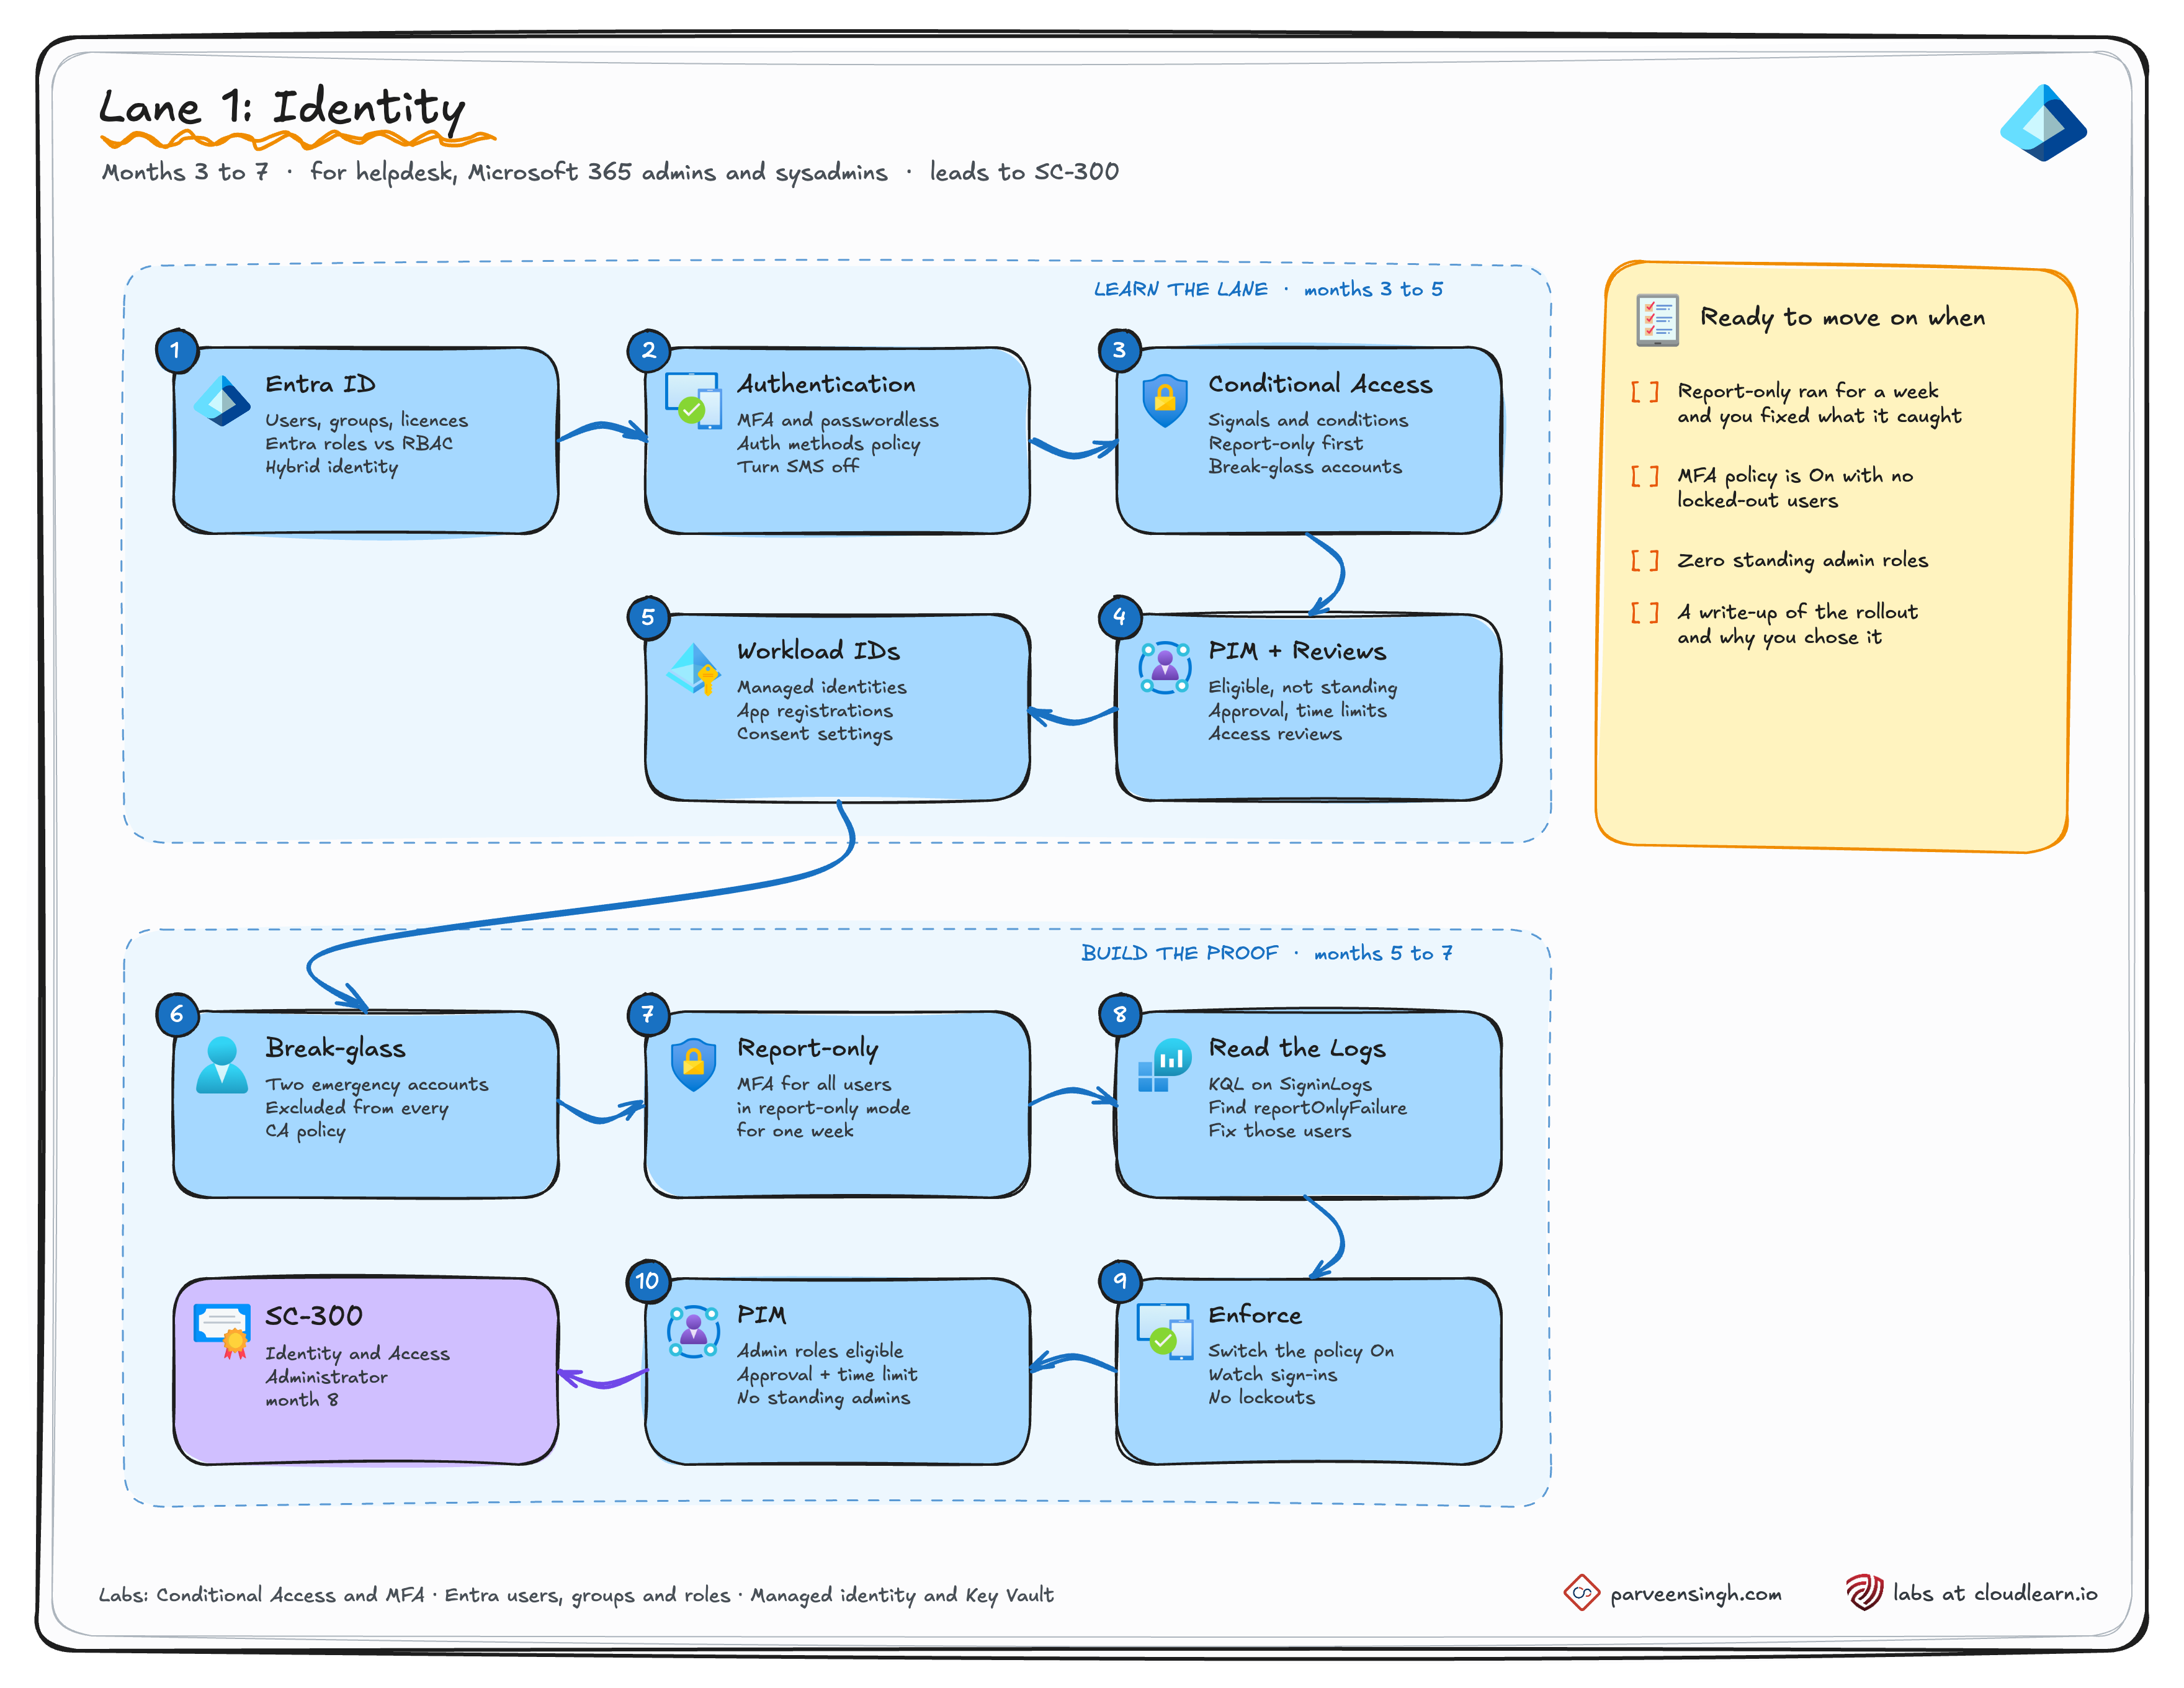
Cert: SC-300. Its skill areas are user identities (20–25%), authentication and access management (25–30%), workload identities (20–25%) and identity governance (20–25%).
| Skill | What "good" looks like |
|---|---|
| Conditional Access | Policies tested in report-only mode before they're enforced, with documented exclusions such as break-glass accounts |
| Authentication methods | MFA for everyone, passwordless for admins, SMS turned off where possible |
| Privileged Identity Management | No standing admin roles. Admins activate a role when they need it, with approval and a time limit. |
| Access reviews | Group and role memberships reviewed on a schedule, not only when someone leaves |
| Workload identities | Managed identities instead of secrets for apps and automation |
Proof project: Conditional Access, rolled out safely
| Step | What you do |
|---|---|
| 1 | Create two break-glass accounts and exclude them from every Conditional Access policy |
| 2 | Create a policy that requires MFA for all users, in report-only mode |
| 3 | Check the sign-in logs to see who the policy would have blocked |
| 4 | Fix the gaps, then switch the policy to On |
| 5 | Make your admin roles eligible in PIM instead of permanently assigned |
| 6 | Write up what you changed, what report-only caught, and why |
Step 3 is the part interviewers care about. If your sign-in logs go to a Log Analytics workspace, this KQL shows what each report-only policy would have done:
SigninLogs
| where TimeGenerated > ago(7d)
| mv-expand Policy = ConditionalAccessPolicies
| where tostring(Policy.result) startswith "reportOnly"
| summarize SignIns = count() by PolicyName = tostring(Policy.displayName), Result = tostring(Policy.result)
| order by PolicyName asc, SignIns desc
reportOnlyFailure rows are the sign-ins the policy would have blocked. Those are the users to fix before you switch the policy on. If you report MFA numbers to anyone, Your MFA Coverage Number Is Probably Wrong covers how to get one you can defend.
Labs:
| Lab | Covers |
|---|---|
| Configure Conditional Access Policies and MFA in Microsoft Entra ID | Steps 2 to 4 |
| Microsoft Entra ID: Create Users, Groups and Assign Roles | Users, groups and role assignments |
| Securing Azure Web Apps with Managed Identity and Key Vault | Workload identities |
Stages 2 and 3, Lane 2: Cloud Platform Security
Learn the lane: months 3 to 5. Build the proof: months 5 to 7.
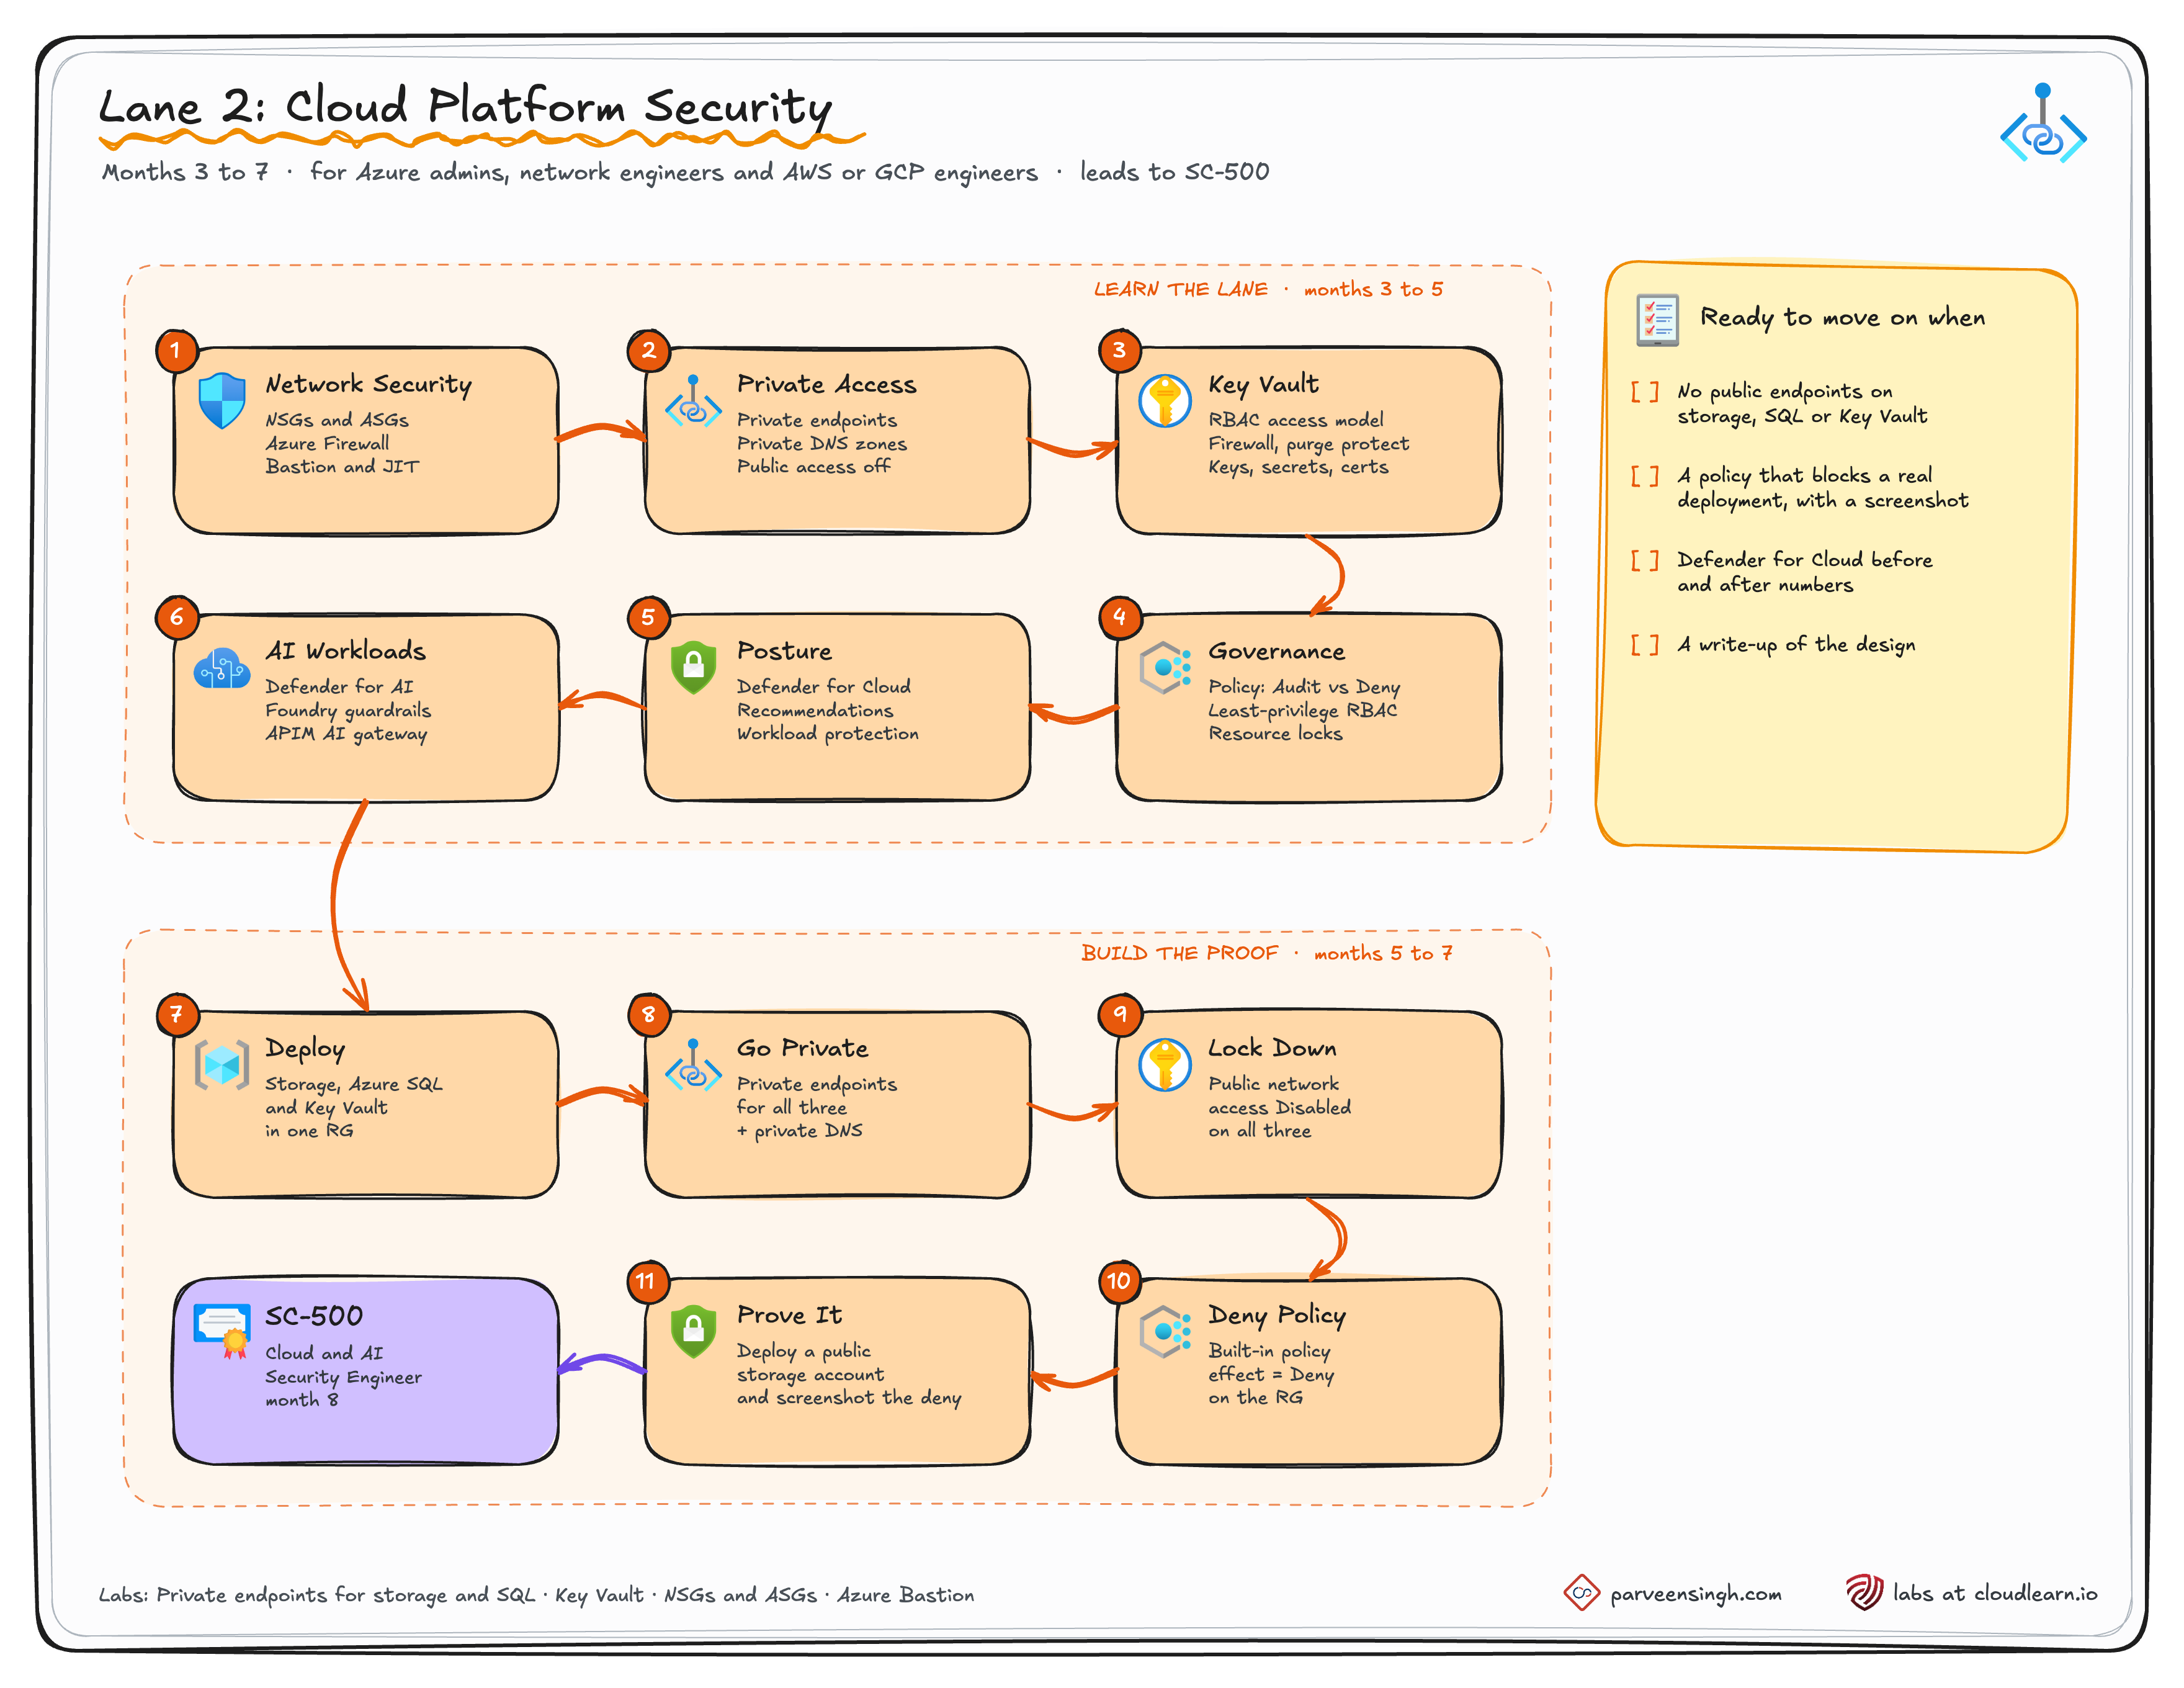
Cert: SC-500. Its skill areas are identity, access and governance (20–25%), storage, databases and networking (25–30%), compute including AI (20–25%), and security posture (20–25%).
| Skill | What "good" looks like |
|---|---|
| Network segmentation | NSGs and application security groups, with no management ports open to the internet |
| Private access to PaaS | Private endpoints for storage, SQL and Key Vault, with public network access disabled |
| Secrets | Key Vault with RBAC, no public access, and apps reading secrets through managed identities |
| Governance | Azure Policy that denies insecure deployments, not only reports on them |
| Posture | Defender for Cloud recommendations worked down, with workload protection plans turned on where they matter |
| AI workloads | Defender for AI services enabled, Foundry guardrails configured, AI APIs behind API Management |
Proof project: one app with no public endpoints
| Step | What you do |
|---|---|
| 1 | Deploy a storage account, an Azure SQL database and a Key Vault into one resource group |
| 2 | Add private endpoints for all three, with private DNS zones |
| 3 | Disable public network access on all three |
| 4 | Assign an Azure Policy that denies storage accounts with public network access |
| 5 | Try to deploy a public storage account and capture the deny |
| 6 | Write up the design, and what Defender for Cloud showed before and after |
Steps 2 and 3 for Key Vault look like this. Storage uses --group-id blob and SQL uses --group-id sqlServer:
KV_ID=$(az keyvault show --name kv-proof-01 --resource-group rg-sec-proof --query id -o tsv)

az network private-endpoint create \
  --name pe-kv-proof-01 \
  --resource-group rg-sec-proof \
  --vnet-name vnet-sec-proof \
  --subnet snet-private-endpoints \
  --private-connection-resource-id "$KV_ID" \
  --group-id vault \
  --connection-name kv-proof-01-conn

az keyvault update --name kv-proof-01 --resource-group rg-sec-proof --public-network-access Disabled
Steps 4 and 5 use a built-in policy, Storage accounts should disable public network access. Its default effect is Audit, so set it to Deny:
az policy assignment create \
  --name deny-public-storage \
  --display-name "Deny storage accounts with public network access" \
  --policy b2982f36-99f2-4db5-8eff-283140c09693 \
  --scope "/subscriptions/`<subscription-id>`/resourceGroups/rg-sec-proof" \
  --params '{ "effect": { "value": "Deny" } }'

# This should now fail with RequestDisallowedByPolicy
az storage account create \
  --name stpublictest$RANDOM \
  --resource-group rg-sec-proof \
  --public-network-access Enabled
That failed deployment is your screenshot. One policy blocking a real deployment says more in an interview than a slide about governance.
Pro tip: Policy assignments can take a few minutes to take effect. If the test deployment succeeds straight away, wait and try again before you debug the policy.
Labs:
| Lab | Covers |
|---|---|
| Azure Private Endpoints: Lock Down Your Storage and SQL | Steps 2 and 3 |
| Deploying and Managing Azure Key Vault | Key Vault setup and access |
| Implement NSGs and ASGs in Azure | Network segmentation |
| Implementing Secure VM Access with Azure Bastion | VM access without public IPs |
Can you skip AZ-104 and go straight to SC-500? You can book it. But the exam assumes you already run Azure, so learn the admin side first, even if you never sit AZ-104.
Stages 2 and 3, Lane 3: Security Operations
Learn the lane: months 3 to 5. Build the proof: months 5 to 7.
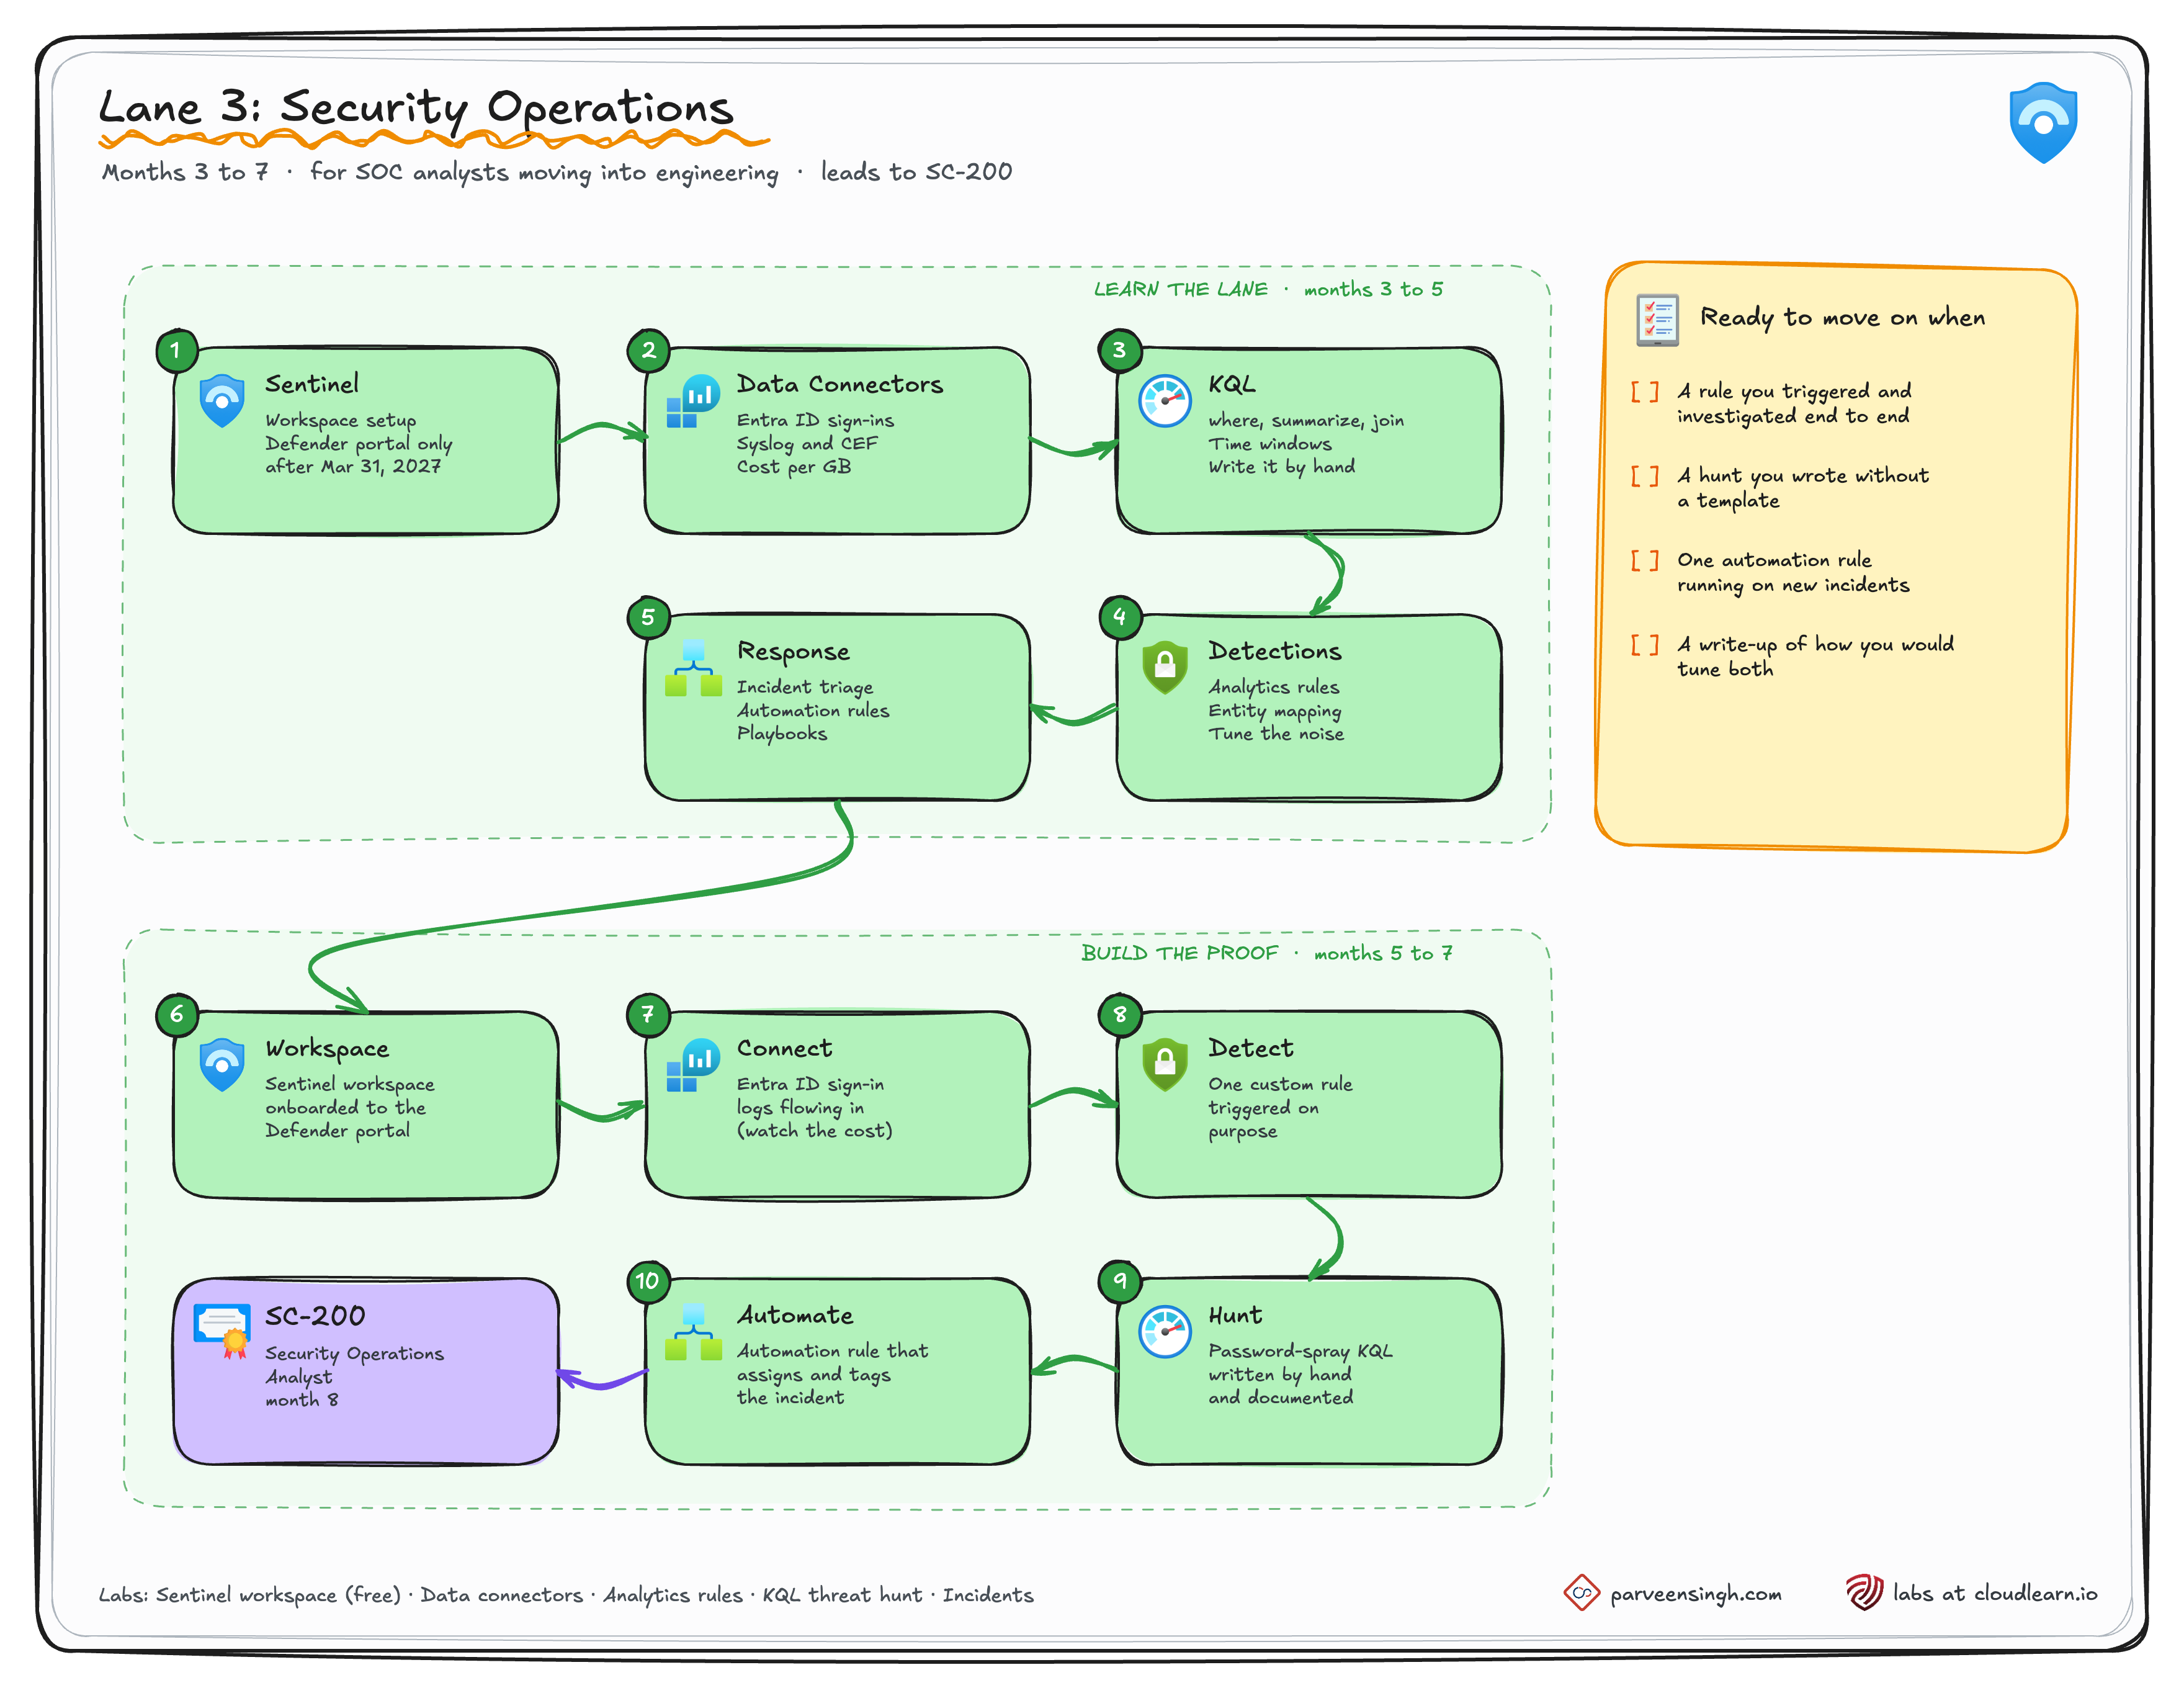
Cert: SC-200. Its skill areas are managing a security operations environment (40–45%), responding to incidents (35–40%) and threat hunting (20–25%).
| Skill | What "good" looks like |
|---|---|
| Sentinel in the Defender portal | A workspace onboarded to the Defender portal, not only the Azure portal |
| Data connectors | The right sources connected, with costs understood before you turn them on |
| Detections | Custom analytics rules with entity mapping, tuned so they don't flood the queue |
| Hunting | KQL written by hand, not only copied from templates |
| Response | Automation rules and playbooks for the incidents you see every week |
Proof project: one detection and one hunt
| Step | What you do |
|---|---|
| 1 | Create a Sentinel workspace and onboard it to the Defender portal |
| 2 | Connect at least one data source, such as Microsoft Entra ID sign-in logs |
| 3 | Write one custom analytics rule and trigger it on purpose |
| 4 | Write one KQL hunt and document what you found, even if it's nothing |
| 5 | Add an automation rule that assigns and tags the incident |
| 6 | Write up the rule logic, the hunt, and how you'd tune both |
Threat hunting is a fifth of SC-200, and writing KQL from scratch is where most people get stuck. A good first hunt is password spraying: one IP address failing sign-ins against many accounts.
SigninLogs
| where TimeGenerated > ago(1d)
| where ResultType != "0"
| summarize FailedAccounts = dcount(UserPrincipalName), Attempts = count() by IPAddress
| where FailedAccounts >= 10
| order by FailedAccounts desc
Write it yourself first, then compare it with the hunting queries in the Sentinel content hub.
Labs:
Stage 4: Certify (Month 8)
The exam goes last, after the project. By then you're confirming something you've already built, and the scenario questions feel familiar because you've hit those problems yourself.
| Lane | Exam | Official study guide | Free practice assessment |
|---|---|---|---|
| Identity | SC-300 | SC-300 study guide | SC-300 practice assessment |
| Cloud platform security | SC-500 | SC-500 study guide | Not available yet. Microsoft says practice assessments usually follow within about 8 weeks of an exam leaving beta. |
| Security operations | SC-200 | SC-200 study guide | SC-200 practice assessment |
How to spend the month:
- Week 1: go through the study guide line by line and mark each skill green (done in your project), yellow (seen it) or red (never touched it).
- Weeks 2 and 3: turn the reds into yellows with Microsoft Learn and the labs in your lane.
- Week 4: take the free practice assessment, review every wrong answer against the docs, then book the exam.
What to expect on the day:
- Associate exams are 100 minutes, or 120 minutes if they include labs. Most have 40 to 60 questions and a passing score of 700.
- You can open Microsoft Learn during associate exams. The clock keeps running, so use it for one or two lookups, not to re-learn a topic.
- Details are on Microsoft's exam duration and experience page.
You're ready to book when: your proof project is finished, every line of the study guide is green or yellow, and you've passed the practice assessment twice in a row (where one exists).
Stage 5: Grow (Year 2 and Beyond)
Once you have one lane, your project and its certification, there are three ways to grow:
| Path | When it makes sense | Next step |
|---|---|---|
| Go deeper in your lane | You enjoy the work and want to be the go-to person for it | Extend your proof project: add access reviews (identity), Defender for Cloud regulatory compliance (platform) or automation playbooks (SecOps) |
| Add a second lane | Your team needs it, or you want to move toward architecture | Pick the lane that touches yours most. Identity and platform security overlap the most. |
| Architect: SC-100 | You've done real work in at least one lane and design security across teams | SC-100 study guide. It needs SC-300, SC-200 or SC-500 first. |
| Data protection: SC-401 | You want to protect data with Microsoft Purview: sensitivity labels, data loss prevention and insider risk | Information Security Administrator. It's its own track. |
Proof Project Checklists
Tick these off as your project grows. When every box in one lane is ticked, book that lane's exam.
Identity (SC-300)
- Two break-glass accounts, excluded from Conditional Access
- An MFA policy run in report-only mode for at least a week
- A KQL query or workbook showing what report-only caught
- The policy switched on, with the gaps fixed first
- Admin roles eligible in PIM, with approval and a time limit
- A write-up of the rollout and the decisions behind it
Cloud platform security (SC-500)
- Storage, SQL and Key Vault deployed with private endpoints
- Public network access disabled on all three
- An Azure Policy assignment with the Deny effect
- A screenshot of the policy blocking a real deployment
- Defender for Cloud recommendations before and after
- A write-up of the design
Security operations (SC-200)
- A Sentinel workspace onboarded to the Defender portal
- At least one data connector
- One custom analytics rule, triggered on purpose
- One KQL hunt, written by hand and documented
- One automation rule
- A write-up of the rule, the hunt and how you'd tune them
The Biggest Mistake
A comment on one of my videos put it perfectly: AZ-900, SC-900, AZ-104 and SC-300 passed, and still on the helpdesk. The certifications aren't the problem. What's missing is the proof. Pick one lane and finish its project before you book the next exam. A project gives you something specific to talk about in an interview, and a fourth badge doesn't.
Start With One Lane
If you are at Stage 1, start with the free Creating Your First Virtual Machine lab. If your foundation is solid, pick your row in the lane table and open the first lab in that lane. Each CloudLearn lab gives you a real Azure environment with guided steps and checks on your work, so you can build the proof project without a subscription of your own or a surprise bill. The Sentinel workspace lab is free, so security operations is the easiest lane to start today. For everything else, the full lab catalog covers identity, networking, Key Vault and Sentinel.
If you're coming from the developer side instead, the AI-200 study guide covers the exam that replaced AZ-204.